Buy campingmap.net ?
We are moving the project
campingmap.net .
Are you interested in purchasing the domain
campingmap.net ?
domain@kv-gmbh.de · 0541-91531010
Buy campingmap.net ?
What is an alternative to iptables?
An alternative to iptables is nftables, which is a newer and more powerful packet filtering framework for Linux. Nftables provides a more user-friendly syntax and better performance compared to iptables. It also offers additional features such as stateful firewalling, easier rule management, and better integration with the Linux kernel. Overall, nftables is a modern replacement for iptables and is recommended for those looking for a more advanced and efficient packet filtering solution. **
Hello, I have a question regarding iptables.
Sure, I'd be happy to help. What specific question do you have about iptables? **


Similar search terms for Iptables
Top-Angebote
Products related to Iptables:
-
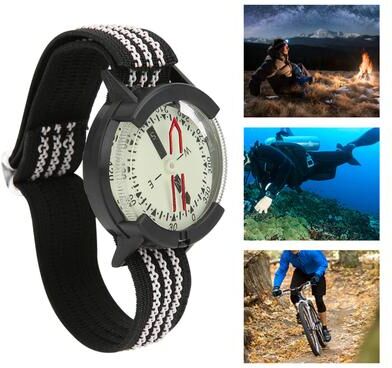
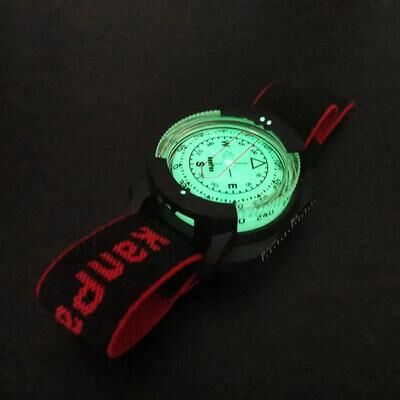
ModernMart Luminous Waterproof Compass Watch For Hiking, Diving & Outdoor Navigation Luminous Waterproof Compass Watch For Hiking, Diving & Outdoor NavigationImagine never secondguessing your direction againwhether you're deep in the forest or exploring underwater. This compact outdoor compass watch is designed for adventurers who need reliable navigation without bulky gear. With its luminous dial and...49,97 $*Shipping: 0,00 $Secure redirect to the provider
-
Multisell Products Hub Waterproof Diving Compass Watch For Scuba Navigation And Outdoor Adventure Waterproof Diving Compass Watch For Scuba Navigation And Outdoor AdventureThis reliable diving compass watch is built for those who refuse to lose direction when it matters most. Whether you are exploring beneath the surface or navigating open waters, this tool keeps you confidently on course. Designed for swimmers,...59,97 $*Shipping: 0,00 $Secure redirect to the provider
-
Multisell Products Hub Tactical Wrist Compass Watch For Hiking, Survival Navigation Gear Tactical Wrist Compass Watch For Hiking, Survival Navigation GearCrafted for those who refuse to get lost, this wrist compass keeps your direction clear when it matters most. Designed for hikers, campers, and outdoor explorers, it delivers reliable navigation without the bulk of traditional gear. The secure strap...59,97 $*Shipping: 0,00 $Secure redirect to the provider
-
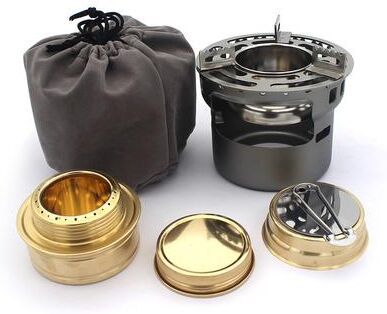
Smart Shopping Spot Portable Stove Burner With Windproof Design For Backpacking & Hiking greyExperience the freedom to cook anywhere with this compact yet powerful portable camping stove built for outdoor adventurers. Designed for hikers, backpackers, and campers, it delivers reliable heat in challenging conditions thanks to its windproof...59,97 $*Shipping: 0,00 $Secure redirect to the provider

-
Why is the port not being allowed in iptables?
The port may not be allowed in iptables because the corresponding rule to allow traffic on that port may not have been added. This could be due to an oversight or mistake in configuring the iptables rules. Additionally, the port may be blocked by a default deny rule in iptables, which prevents any traffic from passing through unless specifically allowed. It's also possible that the service or application listening on that port is not running or is misconfigured, which would prevent iptables from allowing traffic to that port. **
-
How do I block everything except Tor with iptables?
To block everything except Tor with iptables, you can create a rule to allow traffic only through the Tor network. First, allow traffic to the Tor network by adding a rule to allow outbound traffic on the Tor port (usually 9050 or 9150) using the command: ```bash sudo iptables -A OUTPUT -p tcp --dport 9050 -j ACCEPT ``` Then, block all other outbound traffic by adding a rule to drop all other outgoing connections: ```bash sudo iptables -A OUTPUT -j DROP ``` This will ensure that all outbound traffic is blocked except for the traffic going through the Tor network. **
-
How can I use iptables on the Asus RT-AC66U?
To use iptables on the Asus RT-AC66U, you can access the router's web interface by entering its IP address in a web browser. Once logged in, navigate to the "Administration" tab and then select "System" and "Enable JFFS custom scripts and configs." This will allow you to create custom iptables rules in the router's firewall script. You can then add your desired iptables rules to the firewall script to control network traffic according to your preferences. Remember to save your changes and reboot the router for the new rules to take effect. **
-
How can I block the SSH port from outside using iptables?
To block the SSH port (port 22) from outside using iptables, you can use the following command: ``` sudo iptables -A INPUT -p tcp --dport 22 -j DROP ``` This command adds a rule to the INPUT chain of iptables to drop any incoming TCP traffic on port 22, effectively blocking SSH access from outside. Make sure to save the iptables rules so they persist after a reboot by using the `iptables-save` command. Keep in mind that blocking the SSH port may lock you out of your server if you are not careful, so it's important to have an alternative way to access the server in case of any issues. **

What hiking trails are there around Nuremberg?
There are several hiking trails around Nuremberg, including the Franconian Way of St. James, which is a popular pilgrimage route that passes through the city. The Nuremberg Castle Path offers a scenic hike through the surrounding forests and hills, with beautiful views of the city and castle. The Rednitz Valley Trail follows the Rednitz River and is a peaceful route for hikers looking to explore the natural beauty of the area. **
Are there good hiking trails in Germany?
Yes, Germany offers a variety of excellent hiking trails for all levels of hikers. The country is known for its diverse landscapes, including the Black Forest, Bavarian Alps, and Rhine Valley, which provide stunning backdrops for hiking. The well-maintained trails are often marked with signposts and offer opportunities to explore forests, mountains, lakes, and charming villages along the way. Whether you are looking for a leisurely stroll or a challenging trek, Germany has something to offer for every hiker. **
Top-Angebote
Products related to Iptables:
-
ModernMart Adventure Waterproof Compass Watch For Hiking Navigation And Outdoor Survival Adventure Waterproof Compass Watch For Hiking Navigation And Outdoor SurvivalNever lose your sense of direction, even in the wild. This compass watch is built for explorers, hikers, and outdoor enthusiasts who need reliable navigation on the go. Designed as a rugged outdoor survival watch, it combines precision direction...79,97 $*Shipping: 0,00 $Secure redirect to the provider
-
Wakeman Outdoors Folding Campfire Grill Grate With GlovesCook meals over an open flame with this portable folding grill grate built for camping, fire pits, and outdoor adventures. Made from solid iron with a food-safe surface, it arrives fully assembled and ready to use with no seasoning required.47,49 $*Shipping: 0,00 $Secure redirect to the provider
-
ModernMart Luminous Waterproof Compass Watch For Hiking, Diving & Outdoor Navigation Luminous Waterproof Compass Watch For Hiking, Diving & Outdoor NavigationImagine never secondguessing your direction againwhether you're deep in the forest or exploring underwater. This compact outdoor compass watch is designed for adventurers who need reliable navigation without bulky gear. With its luminous dial and...49,97 $*Shipping: 0,00 $Secure redirect to the provider
-
Multisell Products Hub Waterproof Diving Compass Watch For Scuba Navigation And Outdoor Adventure Waterproof Diving Compass Watch For Scuba Navigation And Outdoor AdventureThis reliable diving compass watch is built for those who refuse to lose direction when it matters most. Whether you are exploring beneath the surface or navigating open waters, this tool keeps you confidently on course. Designed for swimmers,...59,97 $*Shipping: 0,00 $Secure redirect to the provider
-
What is an alternative to iptables?
An alternative to iptables is nftables, which is a newer and more powerful packet filtering framework for Linux. Nftables provides a more user-friendly syntax and better performance compared to iptables. It also offers additional features such as stateful firewalling, easier rule management, and better integration with the Linux kernel. Overall, nftables is a modern replacement for iptables and is recommended for those looking for a more advanced and efficient packet filtering solution. **
-
Hello, I have a question regarding iptables.
Sure, I'd be happy to help. What specific question do you have about iptables? **
-
Why is the port not being allowed in iptables?
The port may not be allowed in iptables because the corresponding rule to allow traffic on that port may not have been added. This could be due to an oversight or mistake in configuring the iptables rules. Additionally, the port may be blocked by a default deny rule in iptables, which prevents any traffic from passing through unless specifically allowed. It's also possible that the service or application listening on that port is not running or is misconfigured, which would prevent iptables from allowing traffic to that port. **
-
How do I block everything except Tor with iptables?
To block everything except Tor with iptables, you can create a rule to allow traffic only through the Tor network. First, allow traffic to the Tor network by adding a rule to allow outbound traffic on the Tor port (usually 9050 or 9150) using the command: ```bash sudo iptables -A OUTPUT -p tcp --dport 9050 -j ACCEPT ``` Then, block all other outbound traffic by adding a rule to drop all other outgoing connections: ```bash sudo iptables -A OUTPUT -j DROP ``` This will ensure that all outbound traffic is blocked except for the traffic going through the Tor network. **
Similar search terms for Iptables
-
Multisell Products Hub Tactical Wrist Compass Watch For Hiking, Survival Navigation Gear Tactical Wrist Compass Watch For Hiking, Survival Navigation GearCrafted for those who refuse to get lost, this wrist compass keeps your direction clear when it matters most. Designed for hikers, campers, and outdoor explorers, it delivers reliable navigation without the bulk of traditional gear. The secure strap...59,97 $*Shipping: 0,00 $Secure redirect to the provider
-
Smart Shopping Spot Portable Stove Burner With Windproof Design For Backpacking & Hiking greyExperience the freedom to cook anywhere with this compact yet powerful portable camping stove built for outdoor adventurers. Designed for hikers, backpackers, and campers, it delivers reliable heat in challenging conditions thanks to its windproof...59,97 $*Shipping: 0,00 $Secure redirect to the provider
-
The Handy Homestead Survival Wrist Compass Watch For Outdoor Adventure & Hiking Survival Wrist Compass Watch For Outdoor Adventure & HikingNever lose your way on your adventures again. The wrist compass watch combines a reliable compass with a durable, lightweight design, perfect for explorers, hikers, and outdoor enthusiasts. Built for precision and convenience, it keeps you oriented...39,97 $*Shipping: 0,00 $Secure redirect to the provider
-
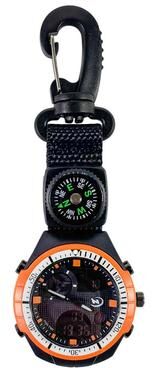
Multisell Products Hub Outdoor Hiking Watch With Compass & Carabiner Survival Sports Pocket Watch For Camping, Hiking, And Backpacking orangeGear up for your next adventure with the Hiking Watch designed for explorers, outdoor enthusiasts, and adventurers alike. This allinone survival gadget combines a precision compass, sports pocket watch, and carabiner for easy attachment to your...44,97 $*Shipping: 0,00 $Secure redirect to the provider
-
How can I use iptables on the Asus RT-AC66U?
To use iptables on the Asus RT-AC66U, you can access the router's web interface by entering its IP address in a web browser. Once logged in, navigate to the "Administration" tab and then select "System" and "Enable JFFS custom scripts and configs." This will allow you to create custom iptables rules in the router's firewall script. You can then add your desired iptables rules to the firewall script to control network traffic according to your preferences. Remember to save your changes and reboot the router for the new rules to take effect. **
-
How can I block the SSH port from outside using iptables?
To block the SSH port (port 22) from outside using iptables, you can use the following command: ``` sudo iptables -A INPUT -p tcp --dport 22 -j DROP ``` This command adds a rule to the INPUT chain of iptables to drop any incoming TCP traffic on port 22, effectively blocking SSH access from outside. Make sure to save the iptables rules so they persist after a reboot by using the `iptables-save` command. Keep in mind that blocking the SSH port may lock you out of your server if you are not careful, so it's important to have an alternative way to access the server in case of any issues. **
-
What hiking trails are there around Nuremberg?
There are several hiking trails around Nuremberg, including the Franconian Way of St. James, which is a popular pilgrimage route that passes through the city. The Nuremberg Castle Path offers a scenic hike through the surrounding forests and hills, with beautiful views of the city and castle. The Rednitz Valley Trail follows the Rednitz River and is a peaceful route for hikers looking to explore the natural beauty of the area. **
-
Are there good hiking trails in Germany?
Yes, Germany offers a variety of excellent hiking trails for all levels of hikers. The country is known for its diverse landscapes, including the Black Forest, Bavarian Alps, and Rhine Valley, which provide stunning backdrops for hiking. The well-maintained trails are often marked with signposts and offer opportunities to explore forests, mountains, lakes, and charming villages along the way. Whether you are looking for a leisurely stroll or a challenging trek, Germany has something to offer for every hiker. **
* All prices are inclusive of VAT and, if applicable, plus shipping costs. The offer information is based on the details provided by the respective shop and is updated through automated processes. Real-time updates do not occur, so deviations can occur in individual cases. ** Note: Parts of this content were created by AI.